Networking / Infrastructure
Personal ProjectPrivate Developer Network
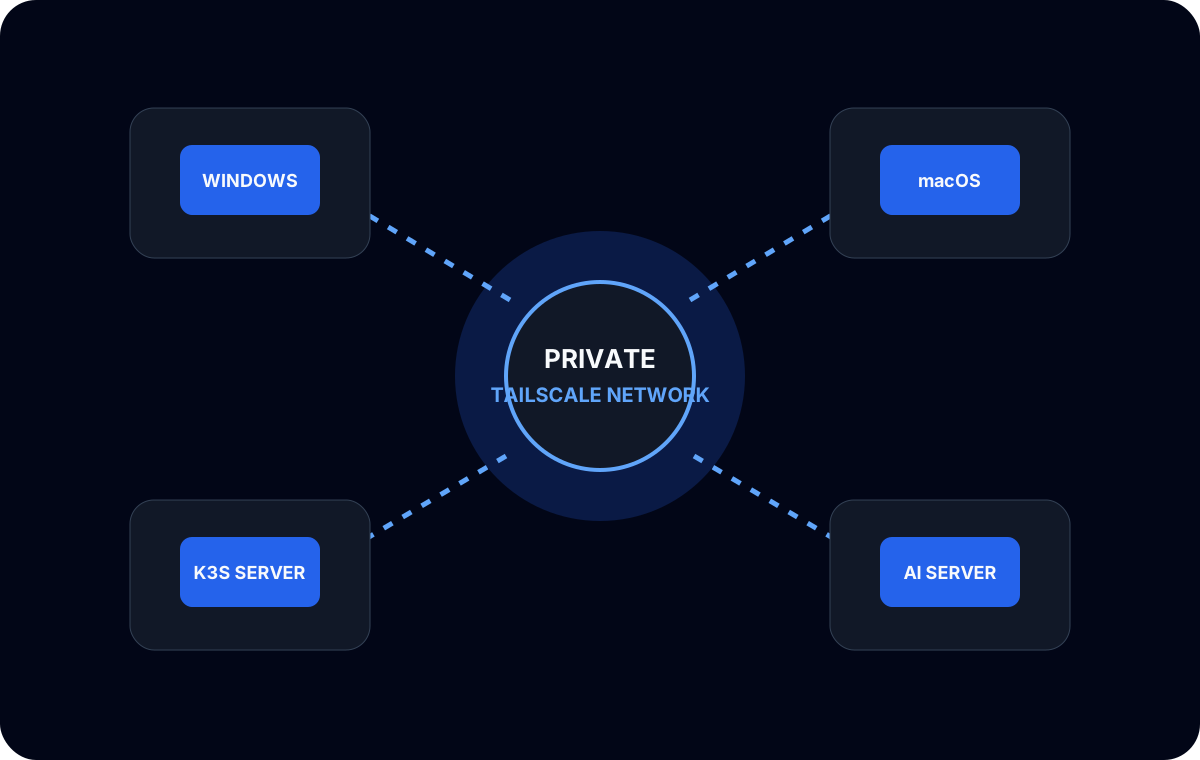
A Headscale-controlled private network that links Windows and macOS workstations with application servers, K3s infrastructure, reverse proxies, and a local AI inference server.
HeadscaleTailscaleCaddyUbuntumacOSWindows
Context
The Problem
Development machines, application infrastructure, and local AI services needed private connectivity across different operating systems without exposing each service directly to the public internet.
System flow
Architecture
Windows Workstation
macOS Workstation
Headscale Control Server
Tailscale Network
K3s Server
AI Server
Applications
Local LLMs
Implementation
Engineering
- Set up a self-hosted Headscale control server for a Tailscale-compatible private network.
- Used authentication keys to enroll Windows and macOS machines, application servers, and K3s infrastructure.
- Enabled private access to local AI inference and application services.
- Connected Caddy reverse-proxy routes across the private network.
- Investigated routing and connectivity across heterogeneous machines and services.
What required care
Challenges
- Troubleshooting routing and reachability between workstations, servers, and Kubernetes workloads.
- Coordinating device enrollment and connectivity across Windows, macOS, and Ubuntu.
- Keeping reverse-proxy access aligned with private-network routes.
Technology
Stack
Status: Personal Project
HeadscaleTailscaleCaddyUbuntumacOSWindows